Handle every transfer outside the EU, with a defensible file.
The GDPR Transfer Adequacy module screens each third party's country, decides whether a transfer impact assessment is needed, and keeps your decision on record.
Chapter V, one transfer at a time.
Third parties in dozens of countries
Which ones need a transfer impact assessment, and which are already covered?
Spreadsheets and emails
They don't hold up in front of a regulator or a customer audit.
Chapter V is demanding
Standard Contractual Clauses, supplementary measures, a documented assessment of the destination country.
Adequacy lists change
Data Privacy Framework certifications and adequacy decisions evolve; yesterday's answer may be wrong today.
A clear verdict, then a guided assessment.
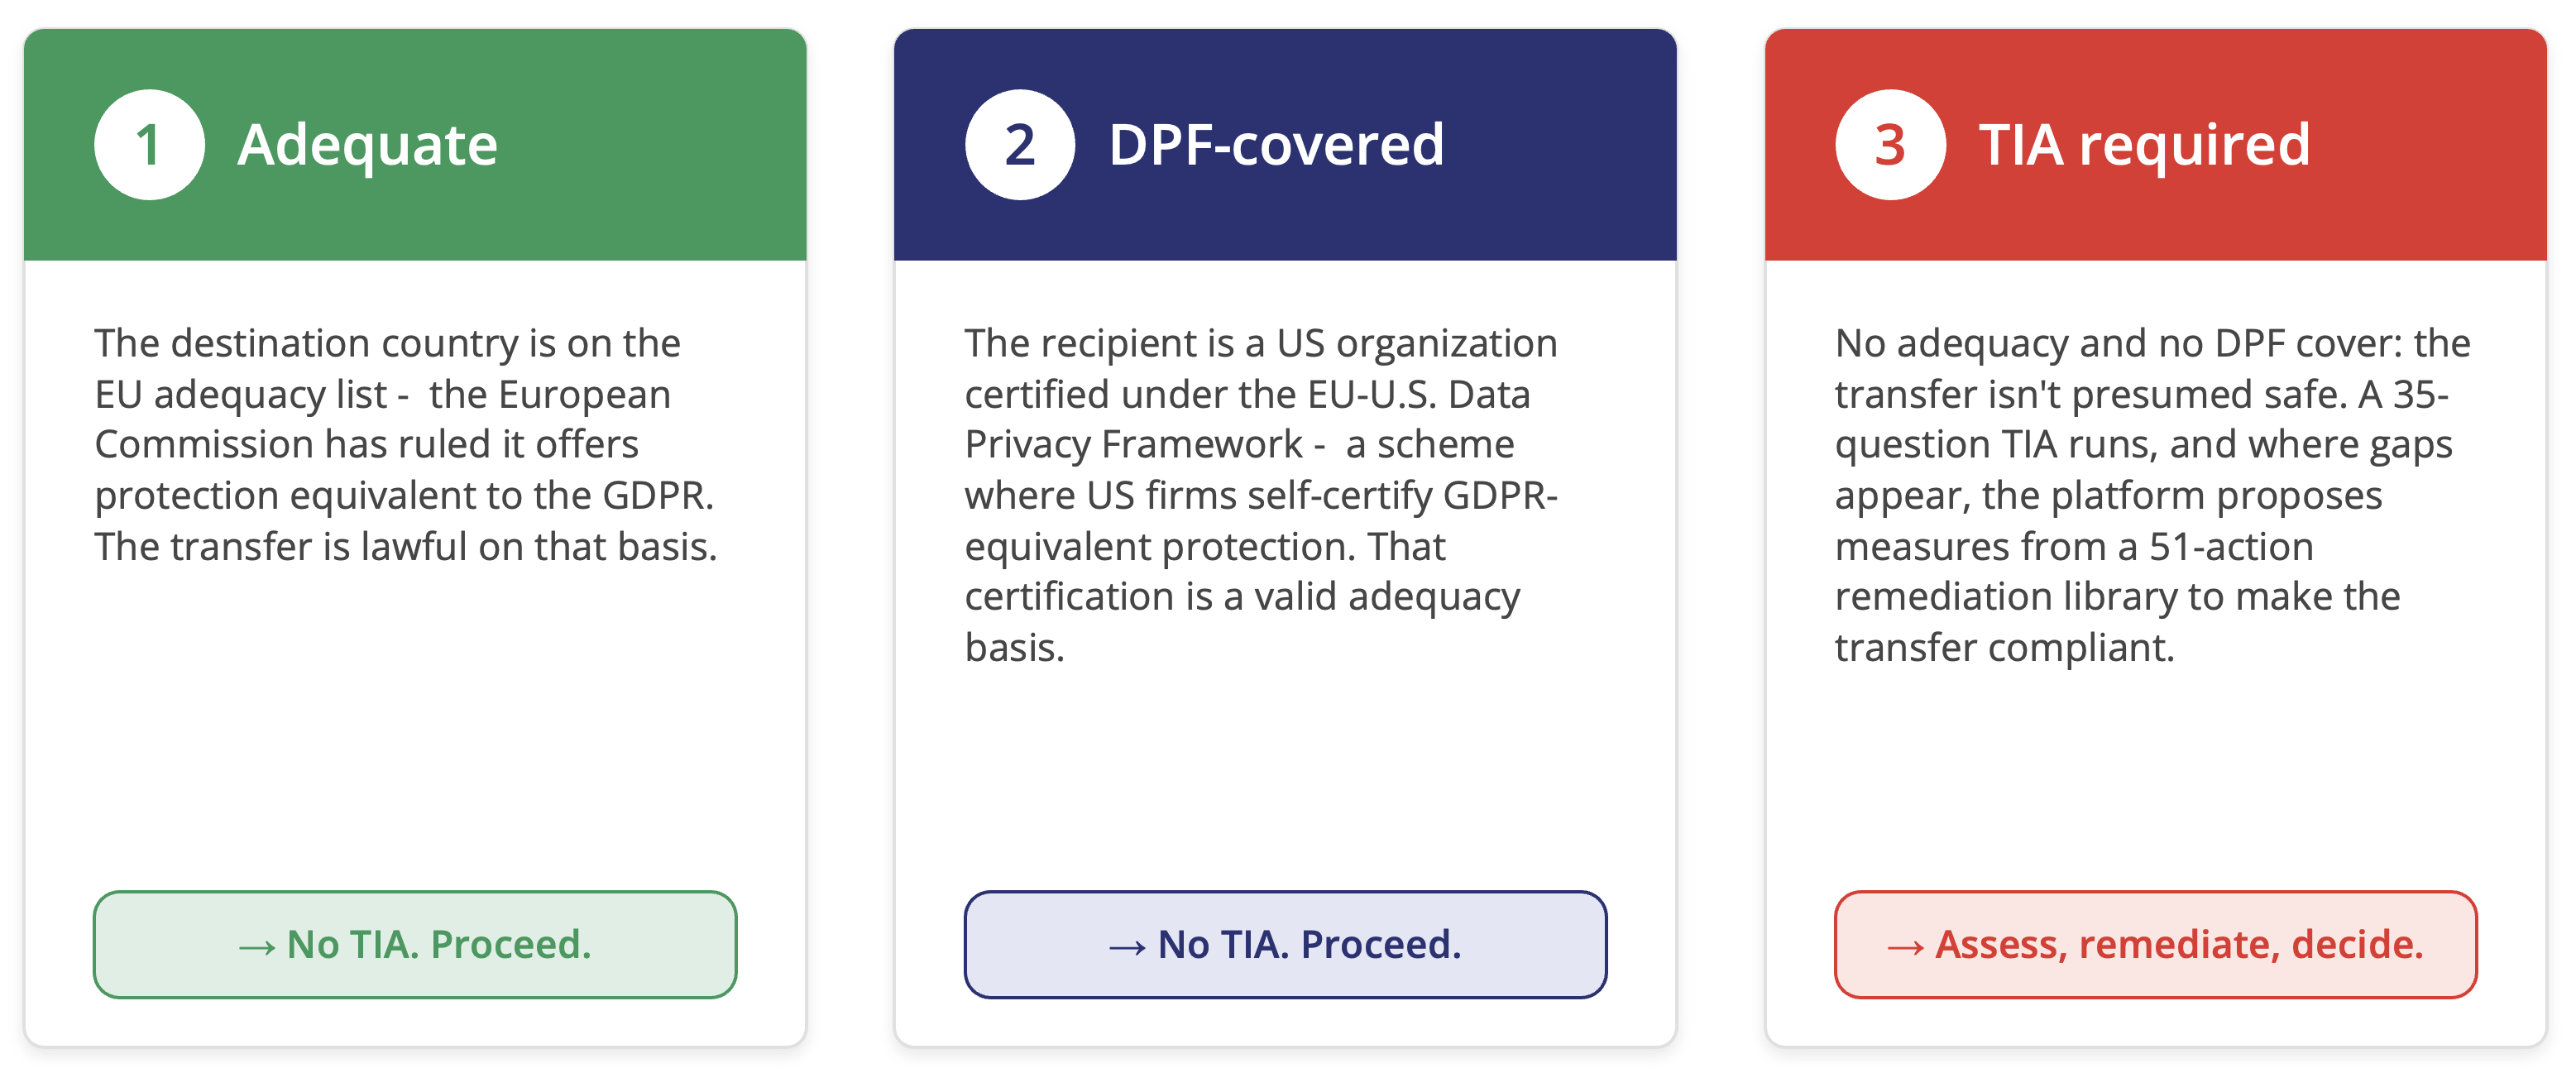
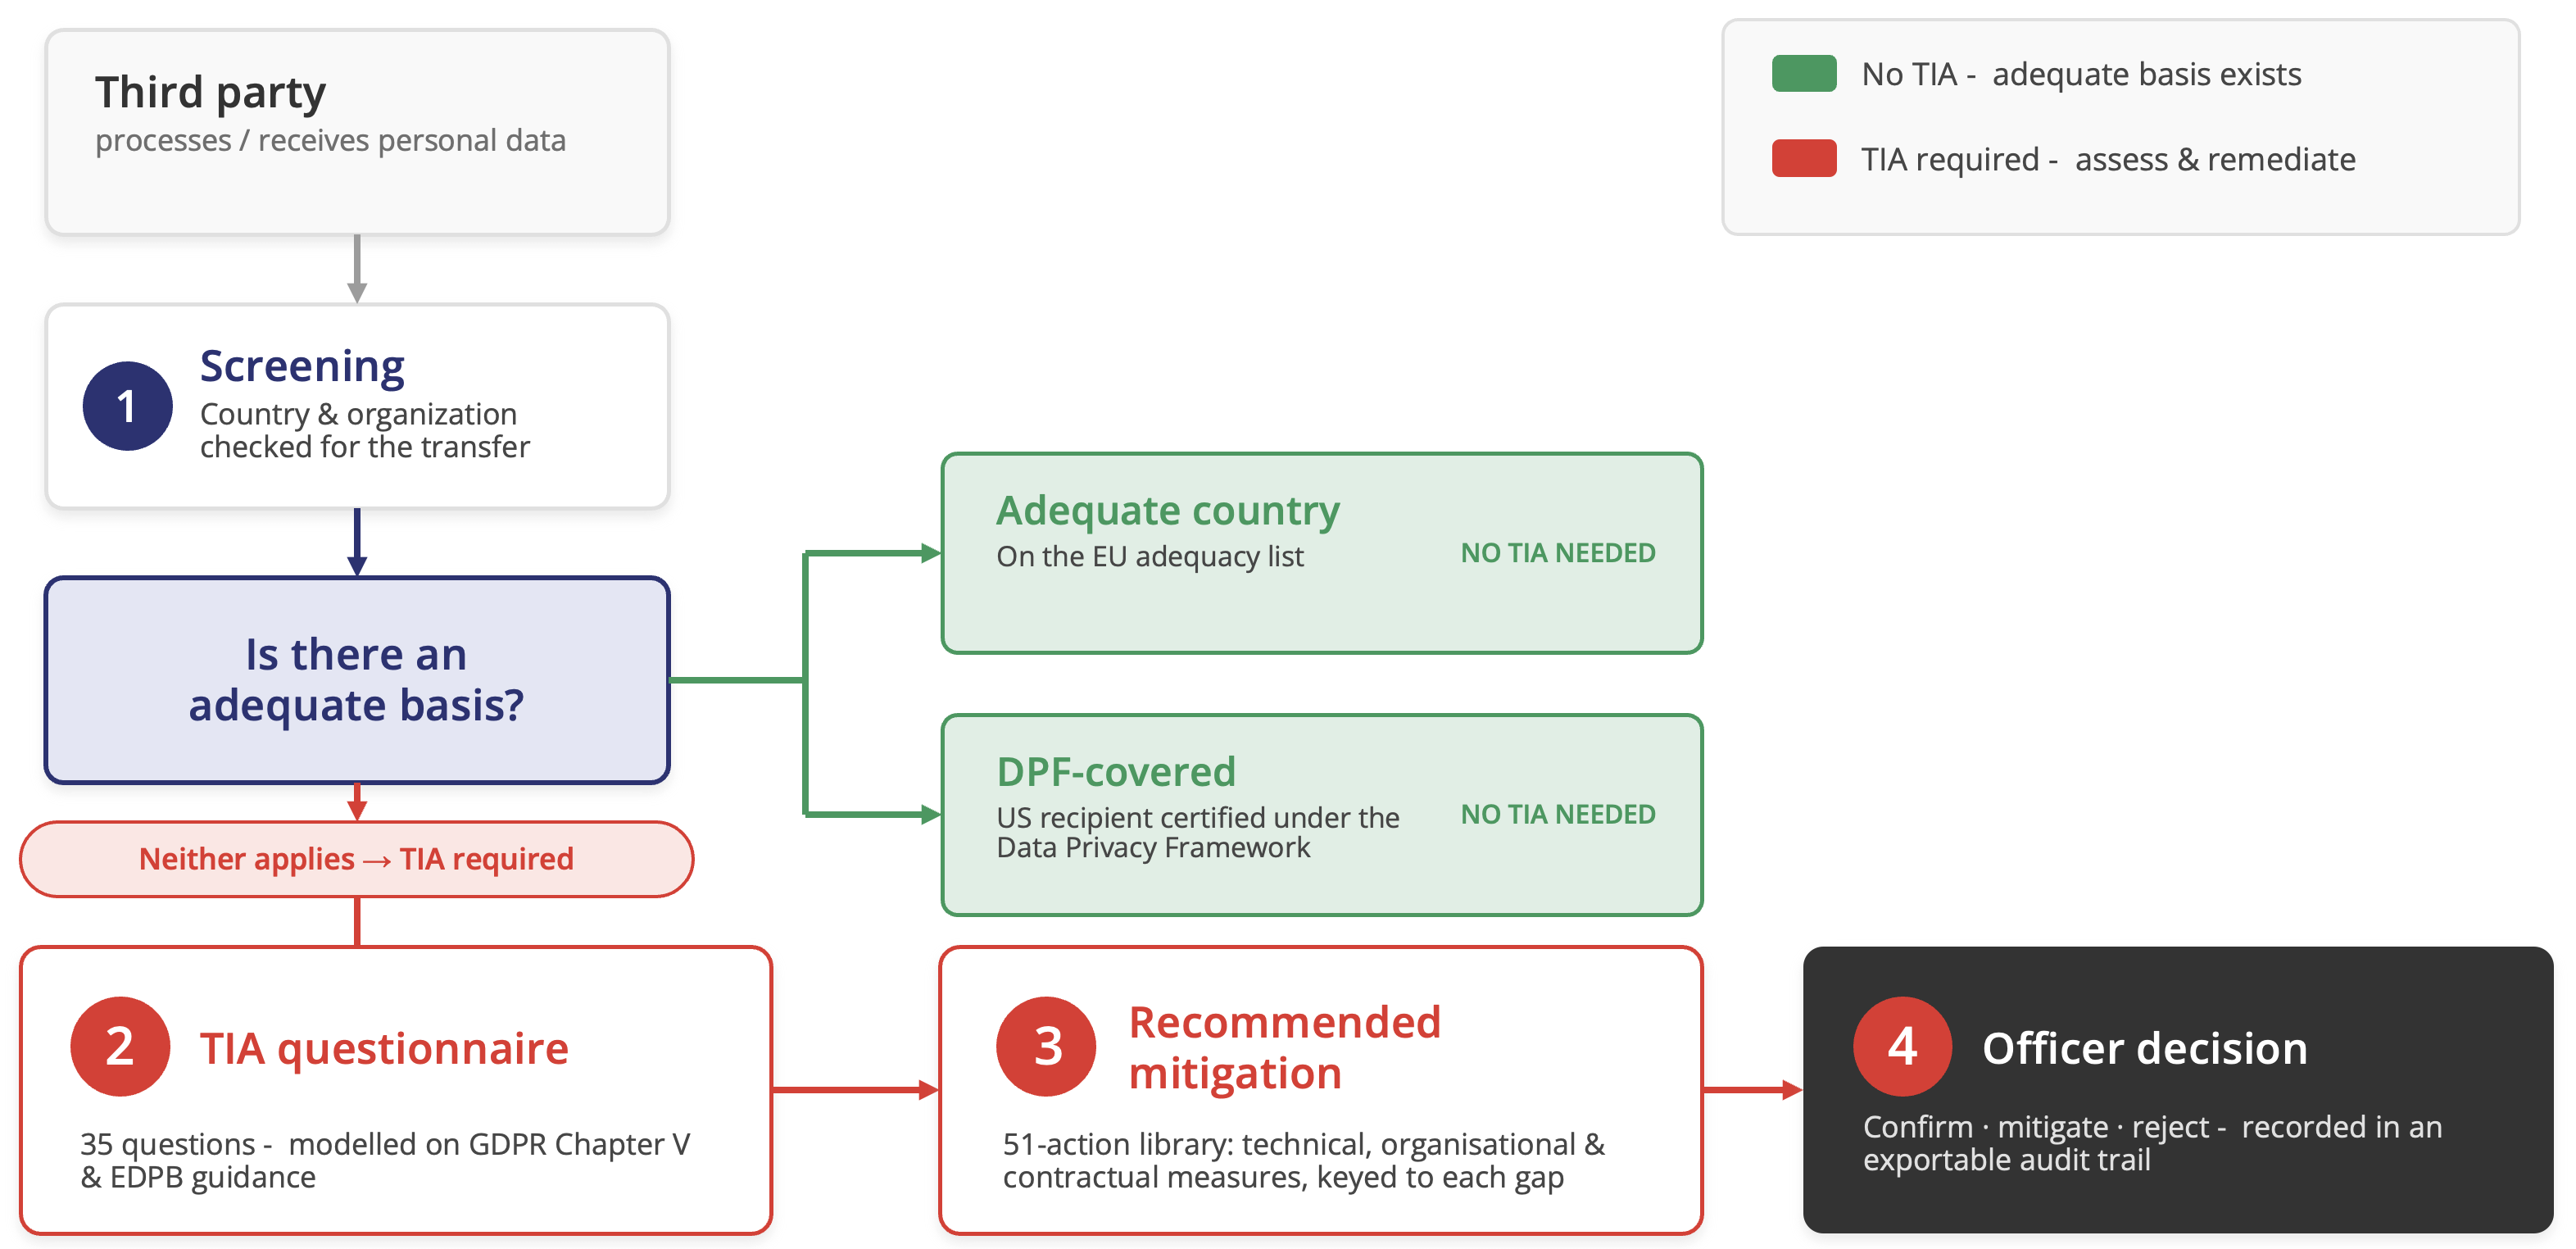
Adequacy screening
Each destination country is checked against the EU adequacy decisions.
Data Privacy Framework registry
EU–U.S. Data Privacy Framework certifications are kept up to date automatically.
Guided TIA
35 questions modelled on GDPR Chapter V and EDPB guidelines when no adequacy basis exists.
51 remediation actions
Standard Contractual Clauses, additional technical and organisational safeguards, or a decision not to transfer.
Your decision on record
The DPO confirms, corrects or rejects the machine's verdict, and the decision is traced.
Your own data under control
The platform stores its data in Zurich, Switzerland, a country with an EU adequacy decision.
From adequacy screening to your decision.
A transfer file you can stand behind.
- A defensible file for each transfer outside the EU
- Review time spent on the cases that need judgment
- A clear verdict: no assessment needed, or assessment required
- Your decision on record and tracked to closure
Frequently asked questions
When is a transfer impact assessment required?
When the destination country has no EU adequacy decision and the recipient is not covered by the Data Privacy Framework. In that case the platform never presumes the transfer is safe: it requires an assessment.
Does the DPO keep the final say?
Yes. Confirm, correct or reject: the human decision sits above the machine's verdict.
Is this module separate from the TPRM assessment?
Yes, it is a separate module. Choose it alone, or together with TPRM Risk Assessment in the Full and Enterprise plans.