Third-party assessment, proportionate to the risk.
From automated screening to in-depth due diligence, then continuous monitoring and remediation • one workflow, calibrated to the risk each third party actually poses.
Data stored in Zurich, Switzerland
One workspace, the whole third-party lifecycle.
From screening to enhanced due diligence • every phase, tracked and scored in one place.
Not every third party needs the same approach.
One risk-assessment platform, applied to every third-party relationship: established partners, spot checks & screening, and third parties subject to GDPR transfer adequacy.
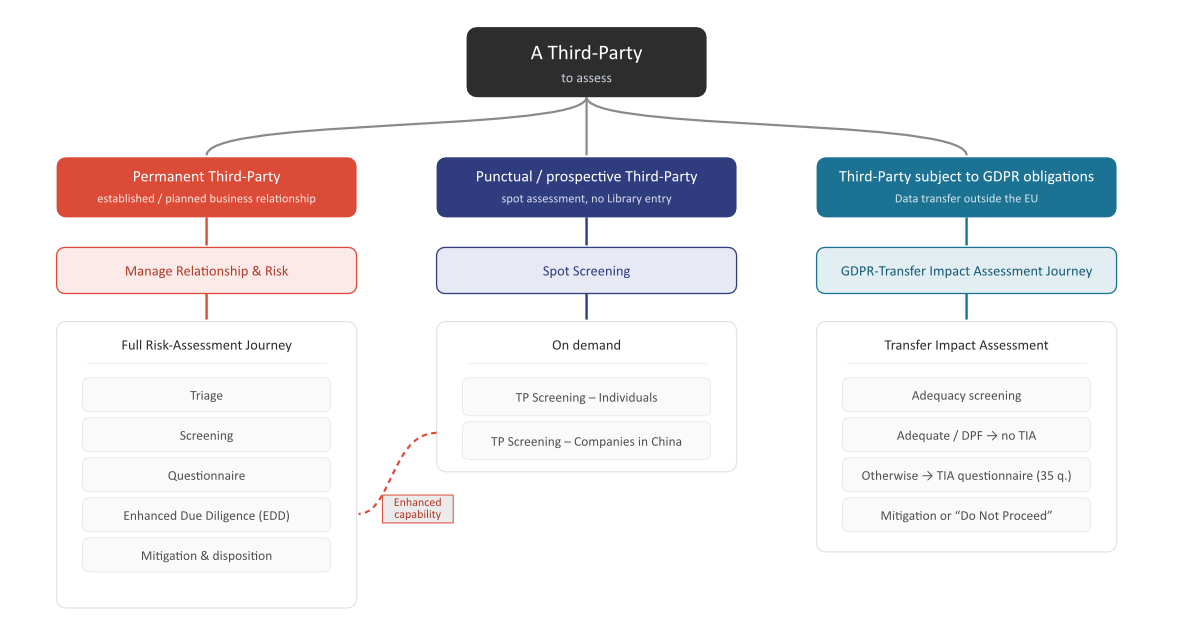
Established third parties • relationship management
Your recurring suppliers and partners follow a complete journey: profiling, graded assessment, continuous monitoring and remediation.
Path 2Spot screening • prospects & individuals
For a one-off partner, an individual or a Chinese counterparty, a targeted check even when intelligence is hard to collect.
Path 3GDPR-scoped third parties • data transfers
For third parties involving transfers outside the EU, the platform documents the transfer impact assessment and adequacy.
A fragmented, partial approach • siloed initiatives across the organization
Compliance, Procurement and Finance each address one part of a third party's assessment, but in isolation • not centralized or coordinated. Ethicaline-TPRM provides a single unified repository and shared assessment processes between internal stakeholders.
Assessment proportionate to the third party and the established business relationship
Initial profiling/triage: country, sector, nature of the relationship, business volume, determines an initial exposure and risk assessment and thus the right assessment program.
Automated screening
Sanctions lists (OFAC, EU, UN), AML/CFT, PEP and adverse media. Instant scoring and alert on any match.
Interactive assessment
Questionnaire sent directly to the third party, document and certification collection in a secure space, consolidated scoring.
Enhanced due diligence
Triggered when the score requires it: in-depth documentary investigation, on-site enquiry and a structured investigation report.
From listing to monitoring, continuous follow-up of the business relationship.
Each third party is assessed according to its risk level; initially identified by triage, with the right level of assessment and monitoring.
A central repository to run your whole program.
Central third-party repository
One source of truth: every third party, its risk profile, history and documents in one place.
Document collection
Request, receive and validate compliance evidence directly from the third party, in a structured way.
Task management
Assessment workflow, deadlines and statuses. Every step is assigned, tracked and closed with evidence.
Delegation & ownership
Assign responsibility for a third party or action to the right team • procurement, legal, compliance.
Continuous monitoring
Permanent re-screening of sanctions and media. Scores update and notify owners the moment an alert appears.
Periodic reassessment
Reassessment campaigns scheduled by risk policy, with automatic reminders and progress reporting.
Built for the obligations that apply to you, in many jurisdictions.
Sapin II, LkSG and FCPA, and a CS3D-ready platform. Plus the new generation of Asian frameworks: MAS TPRM Guidelines in Singapore, APRA CPS 230 in Australia, supply-chain decrees in China.
A platform built by Compliance Officers & Investigators, not just software vendors.
Built-in investigative expertise
Tier 3 brings real investigative know-how • documentary and on-site • where generic platforms stop at the questionnaire.
Risk-graded approach
Scoring combines country and sector to calibrate effort. No over-assessing low-risk third parties, no blind spots on critical ones.
Platform + advisory
The software structures the program; the Ethicaline team stays on hand for complex, multi-jurisdictional cases.
Why choose Ethicaline TPRM
Third-party risk isn't just a software problem • it's a compliance discipline. Here's what sets us apart.
Built by compliance experts
Ethicaline TPRM is a product of Ethicaline, a Paris-based compliance and investigations firm. It's built by people who practise third-party risk • not just people who write software. That domain expertise is designed into every assessment.
Swiss hosting, GDPR by design
Your application data is stored in Zurich, Switzerland, a country with an EU adequacy decision, on architecture chosen for European data-protection expectations • so your due-diligence tool doesn't create risk of its own.
Risk-based triage
Not every third party needs the same scrutiny. Risk-based triage routes each one into a tailored assessment journey • a light-touch screen for the many, deep due diligence for the few that warrant it • so your team's effort goes where the risk actually is.
The whole journey
From screening to continuous monitoring to remediation, Ethicaline TPRM covers the full third-party lifecycle in one workflow • not a point tool you have to stitch together with others.
Frequently asked questions
Where is my data hosted?
In Zurich, Switzerland, on Supabase infrastructure (AWS, Zurich region). Switzerland benefits from an EU adequacy decision. Data is encrypted in transit and at rest. See the Trust Centre.
Does it connect to our ERP and SSO?
Yes. A secure REST API connects your ERP, procurement and vendor systems, and single sign-on works through Microsoft Entra ID (OIDC). See Integrations & SSO.
Do I have to run a full due diligence on every third party?
No. Risk-based triage routes each third party to a light-touch screening, a collaborative assessment or an in-depth enquiry, depending on the risk it actually poses.
Which regulations does it cover?
Sapin II, LkSG and FCPA, with the platform CS3D-ready, plus the MAS TPRM Guidelines (Singapore) and APRA CPS 230 (Australia). See all regulations.
Does the software decide for me?
No. The software structures the work; the expertise decides. Every decision is yours and is recorded in the audit trail.
How is the price determined?
It depends on the number of third parties you assess each year, the modules you choose (TPRM Risk Assessment, GDPR Transfer Adequacy, or both) and the number of administrators and members. Pricing is on request: tell us your numbers.
Can I request access to my data or its deletion?
Yes. We support data access and deletion requests.
Ready to structure your TPRM program?
See the platform applied to your third parties, your countries and your regulatory obligations.