Third-Party subject to GDPR adequacy, when transferring data outside the EU.
For every third party that receives or processes personal data outside the European Union, Ethicaline TPRM decides whether a Transfer Impact Assessment is required • then documents the legal basis, the remediation and the decision, before any data leaves the EU.
Does this transfer need a TIA?
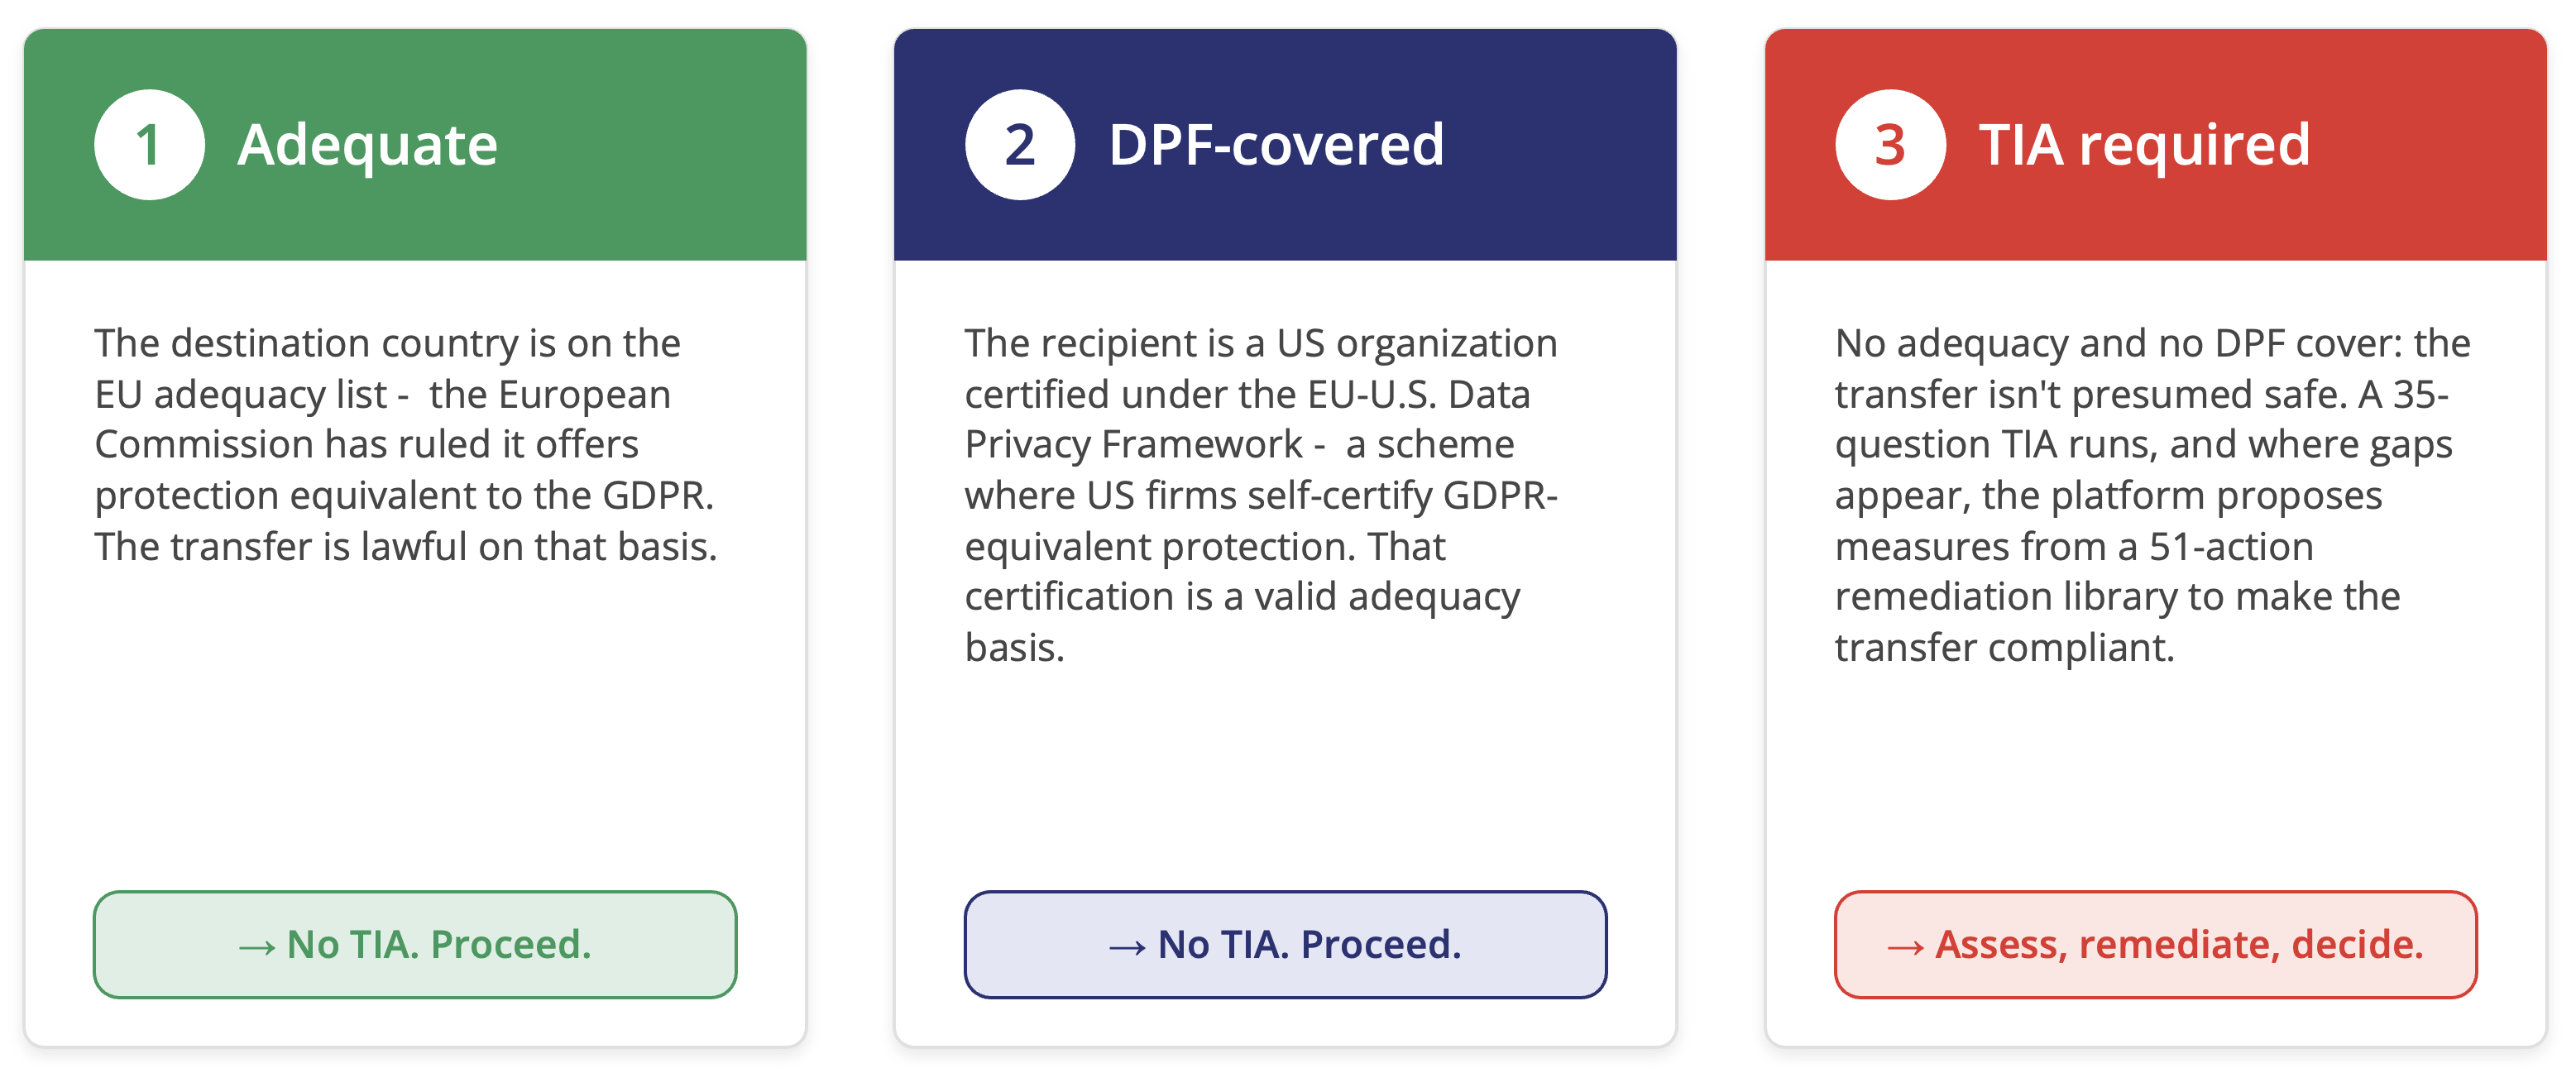
When a third party receives or processes personal data outside the EU, the platform screens the transfer to answer one question: is a Transfer Impact Assessment required, or is there already an adequate legal basis?
Destination covered by an adequacy decision
The destination country is on the EU adequacy list • the European Commission has ruled it offers protection equivalent to the GDPR. The transfer is lawful on that basis.
→ No TIA. Proceed.US recipient certified under the DPF
The recipient is a US organization certified under the EU-U.S. Data Privacy Framework • a scheme where US firms self-certify GDPR-equivalent protection. That certification is a valid adequacy basis, checked against an automatically refreshed registry.
→ No TIA. Proceed.No adequacy and no DPF cover
With no adequacy and no DPF cover, the transfer isn't presumed safe. A 35-question TIA runs, and where gaps appear, the platform proposes measures from a 51-action remediation library to make the transfer compliant.
→ Assess, remediate, decide.A verdict that fails closed: absent adequacy or DPF cover, the platform never presumes a transfer is safe • it requires a TIA, then assesses and remediates.
The TIA, and the actions it triggers.
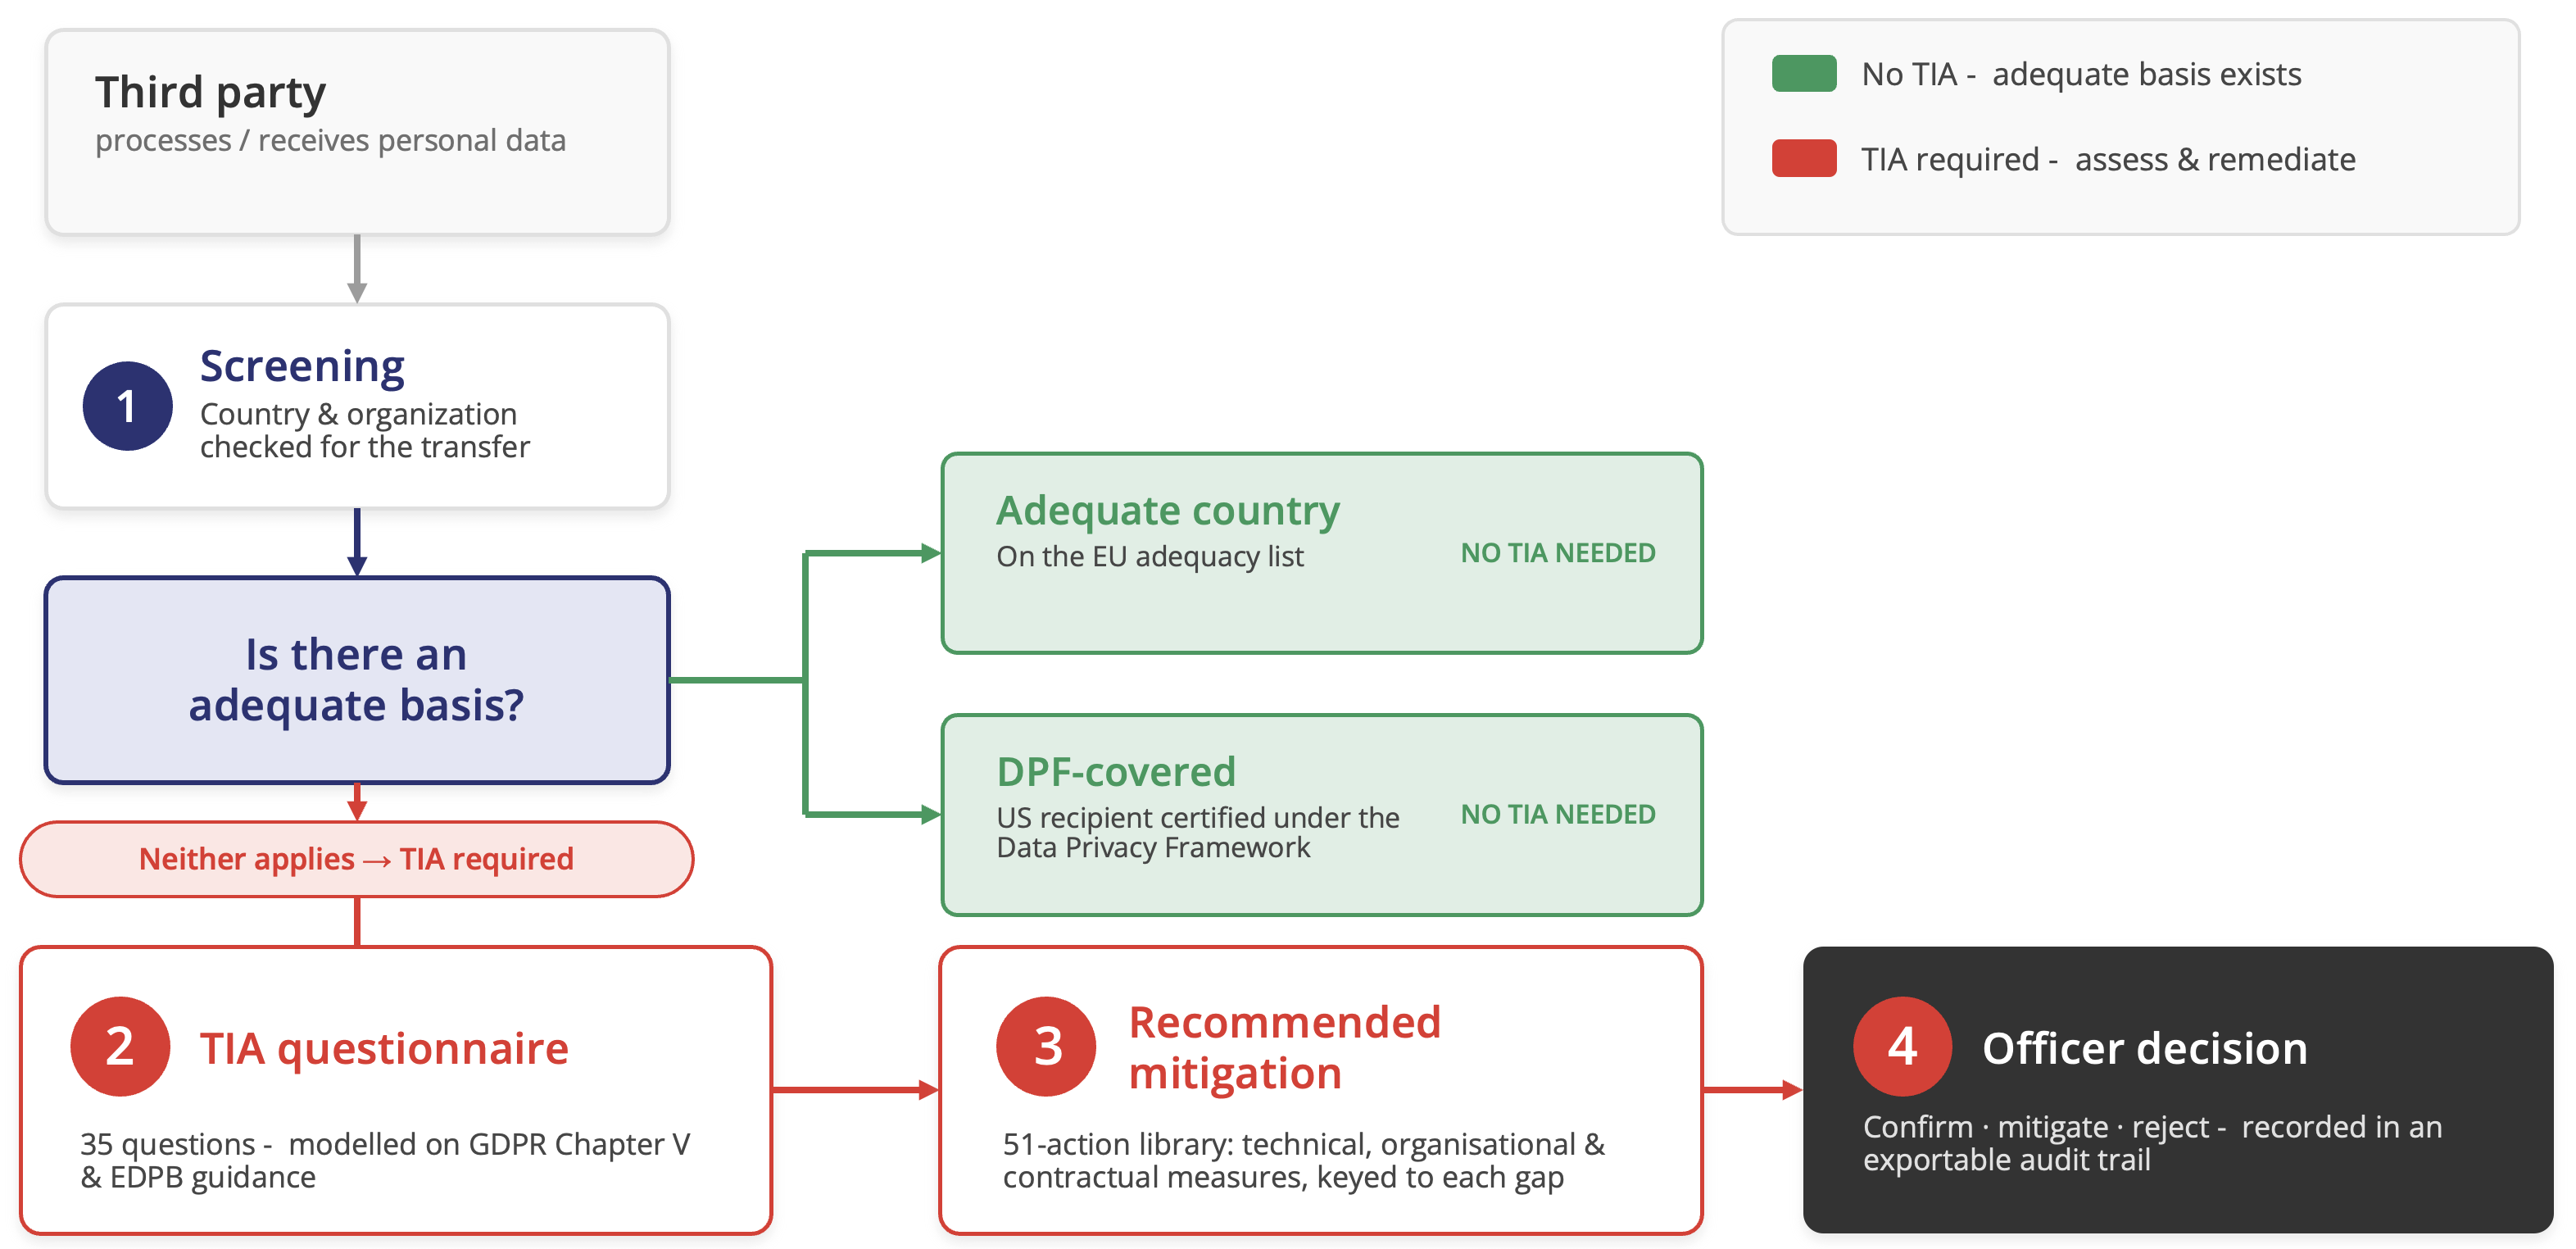
Where a TIA is required, the platform runs a structured assessment built around the regulatory requirements • then proposes the remediation needed to make the transfer lawful.
Regulation-driven questionnaire
35 questions designed to perform the Transfer Impact Assessment • modelled on GDPR Chapter V and EDPB transfer guidance, covering the destination's legal regime, the recipient's safeguards and the nature of the data.
Framework-based remediation
51 actions to make a transfer to a non-EU processor fully GDPR-compliant: Standard Contractual Clauses (SCCs), supplementary technical and organisational safeguards, or, where risk can't be mitigated, a recommendation not to proceed.
DPO decision & audit
A data-protection officer confirms, overrides or rejects the machine verdict. Every step • screening, TIA, decision, remediation • is recorded in a defensible, exportable audit trail.
The objective: for every third party that processes personal data, determine whether a transfer needs a TIA • and, where it does, the remediation actions to undertake so the transfer is lawful.
The TIA workflow: screening to remediation.
How Ethicaline TPRM decides whether a data transfer to a third party needs a Transfer Impact Assessment • and what to do when it does.
Data transfers, assessed and defensible.
Adequacy screening
Every recipient country checked against the EU adequacy decision list.
DPF registry sync
EU-U.S. Data Privacy Framework certifications, refreshed automatically.
Guided TIA
A structured Transfer Impact Assessment when no adequacy basis exists.
Officer decision
Human confirm, override or reject on top of the machine verdict.
Mitigation & SCCs
Standard Contractual Clauses and safeguards tracked to closure.
Bilingual & audit-ready
EN/FR throughout, with an exportable record of every transfer basis.
A transfer outside the EU to secure?
This site uses privacy-first, cookieless analytics and sets no tracking or marketing cookies. Privacy & Cookies